Loading SaaS profile...
Loading SaaS profile...
Detect and stop insider data loss, leaks, and exfiltration.
Monitors endpoint, cloud, and email file movements to track unsanctioned data exfiltration across modern work channels. Prioritizes insider threat severity automatically based on user risk profiles, file sensitivity, and untrusted destination indicators. Triggers automated containment workflows, microlearning training videos, or security analyst escalations. Detects shadow AI usage and source code exposure across public GenAI tools and code repositories.
Agent-based and API cloud monitoring delivers complete file movement visibility without requiring brittle rule management. Context-driven AI scoring distinguishes between everyday legitimate employee collaboration and high-risk data theft. Integrates directly with microlearning tools like Instructor to educate employees in real time upon policy violations. Reduces response latency by executing automated containment actions via SOAR platforms and automated workflows.
Category: Utilities & System Tools
Team Size: 100+
Visit Website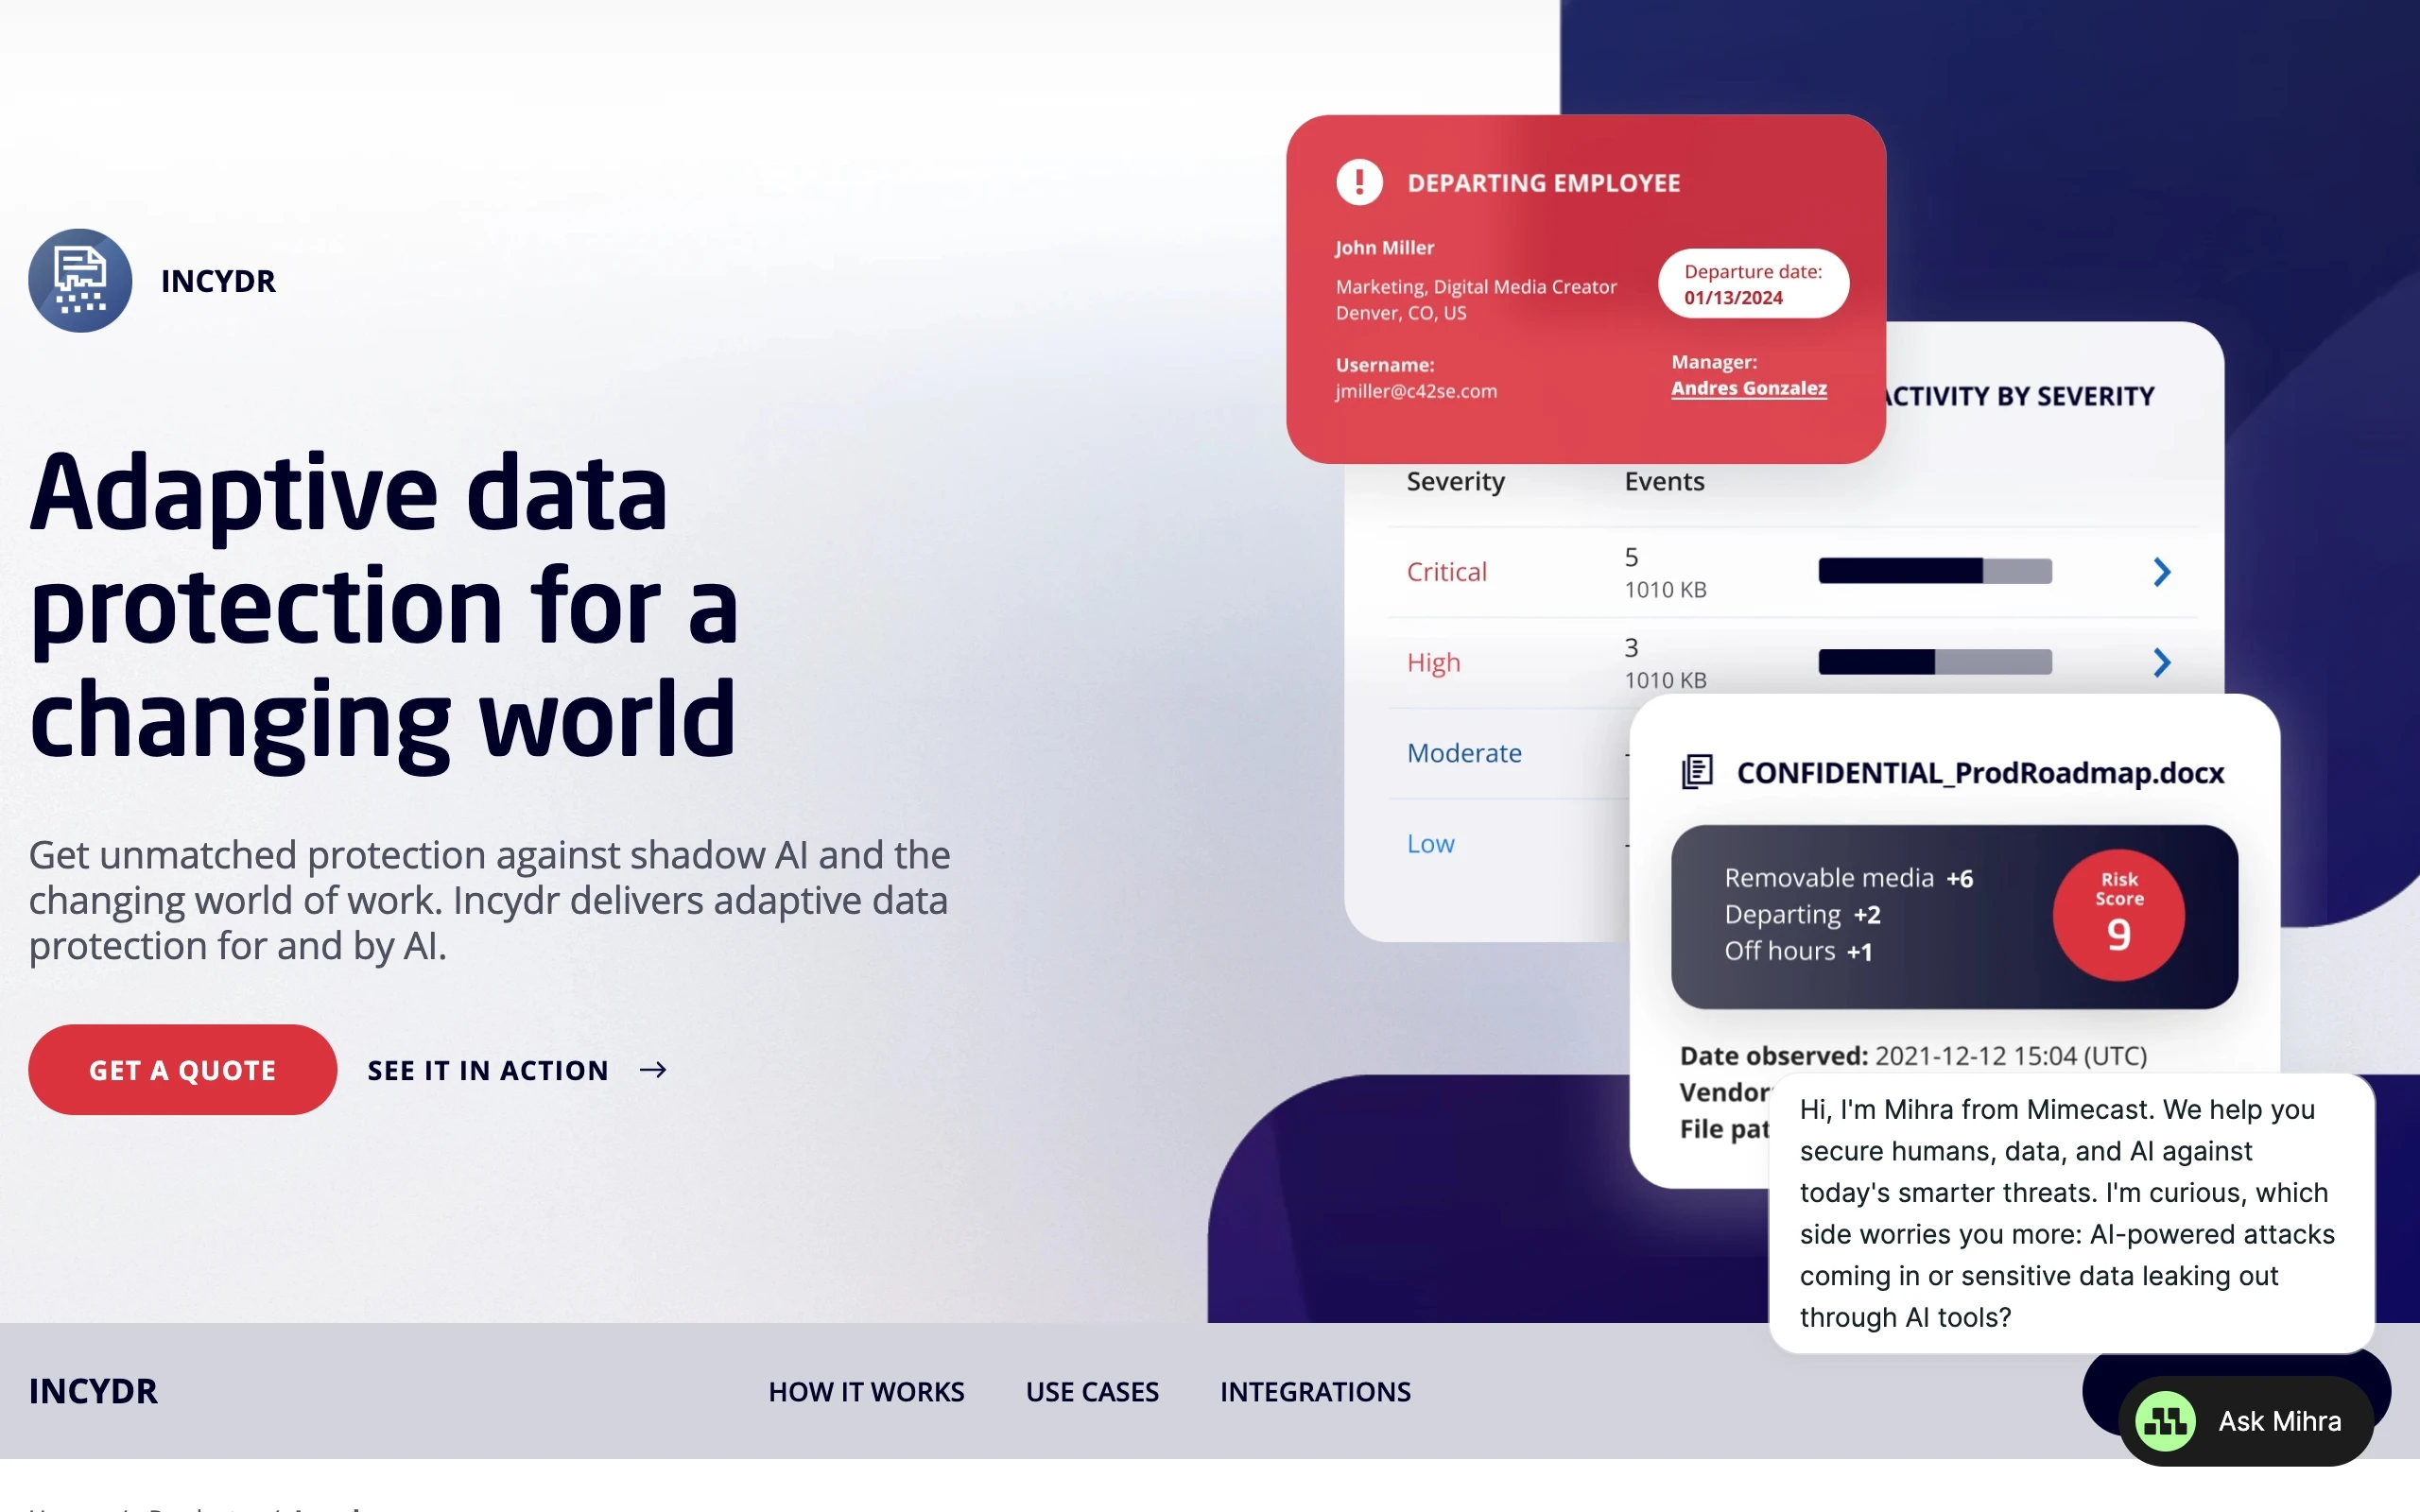
Incydr (by Code42 / Mimecast) is a SaaS insider risk management and data loss prevention platform. It provides complete visibility into employee file movements across endpoints, cloud services, messaging apps, and web destinations without requiring complex block rules. Utilizing AI risk prioritization, Incydr correlates data, user, and destination context to detect file exposure, source code exfiltration, and unauthorized GenAI usage.
Incydr was launched in 2020 by Code42, a Minneapolis cybersecurity firm founded in 2001 by Matthew Dornquast, Brian Bispala, and Mitch Coopet. Developed under CEO Joe Payne to address corporate data theft during remote workforce shifts, Code42 pivoted fully into insider threat management with Incydr before being acquired by Mimecast in 2024.