Loading SaaS profile...
Loading SaaS profile...
Autonomous security scanner proving vulnerabilities and shipping code patches.
Simulates realistic cyber attacks on live application URLs without requiring source code access or SDK installation. Detects common AI app vulnerabilities including IDOR access control bypasses, exposed front-end API keys, and prompt injections. Generates verifiable proof-of-exploit reports to eliminate false positives and alert fatigue for development teams. Produces automated code patches and opens GitHub pull requests to remediate confirmed security flaws immediately.
Tests running web applications from the outside requiring zero source code access or installation friction. Eliminates developer alert fatigue by validating every issue with confirmed proof-of-exploit evidence. Accelerates remediation speed by automatically writing code patches and opening GitHub pull requests. Specifically addresses recurring vulnerabilities introduced by rapid AI generation tools like Cursor and Bolt.
Category: AI & Automation
Team Size: 2-10
Visit Website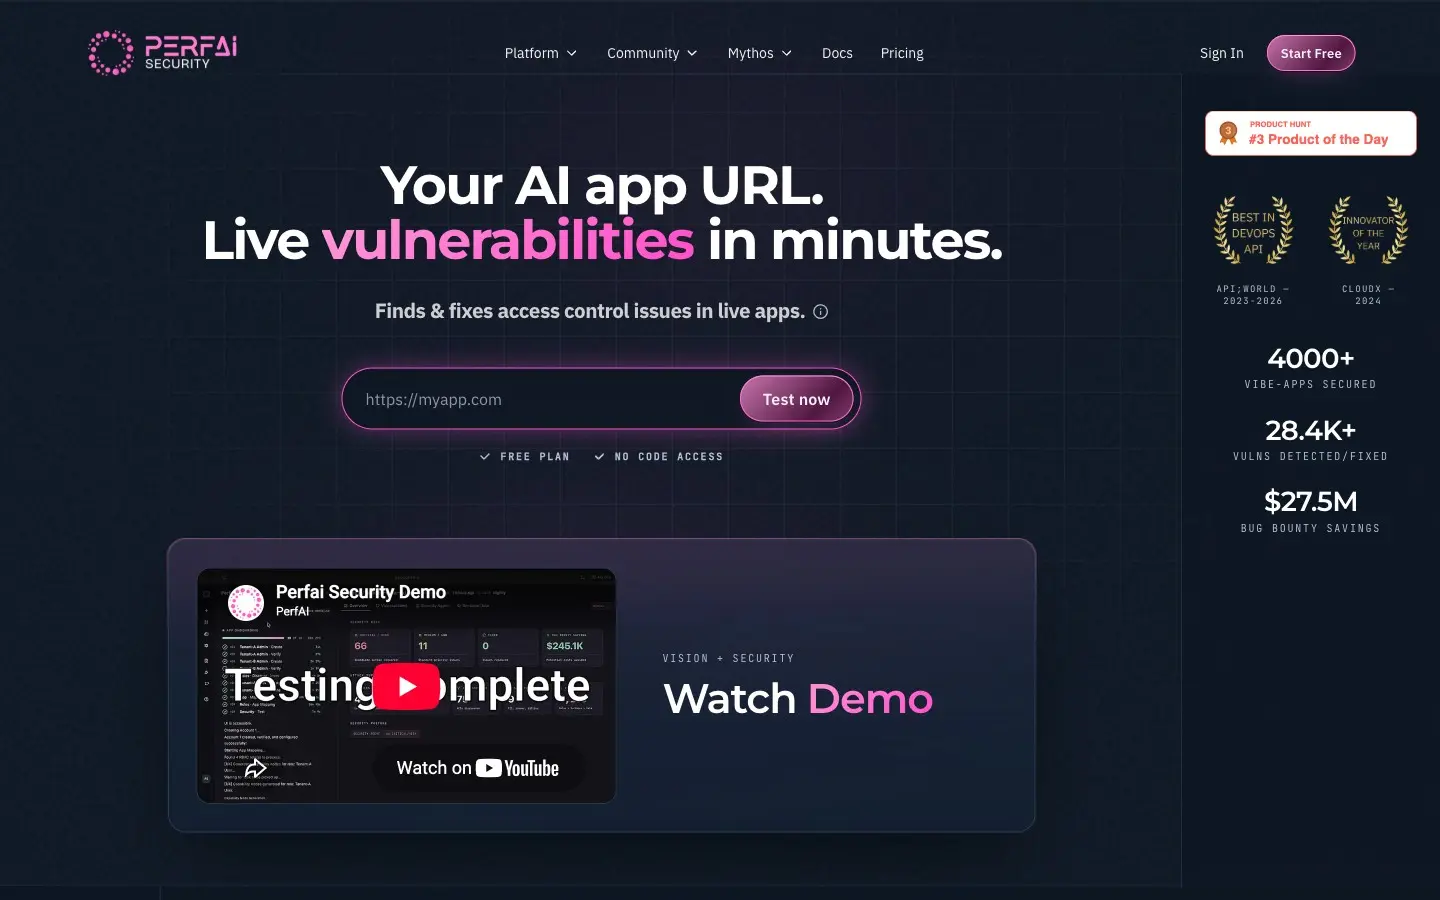
Perfai Security is an AI-powered vulnerability testing platform designed to secure applications built with AI coding assistants like Bolt, Cursor, and v0. By submitting a live application URL, autonomous AI security agents perform non-intrusive attack simulations to detect broken access controls, leaked API keys, authentication bypasses, and prompt injection vulnerabilities. Perfai proves confirmed findings without false positives and automatically generates fix patches and GitHub pull requests.
Perfai Security was developed to address the growing security gaps created by AI-assisted vibe coding. Because AI tools prioritize feature delivery speed over security architecture, apps frequently ship with missing access checks and exposed keys. The team built Perfai Security as an autonomous platform that finds vulnerabilities in live apps and ships code fixes automatically.